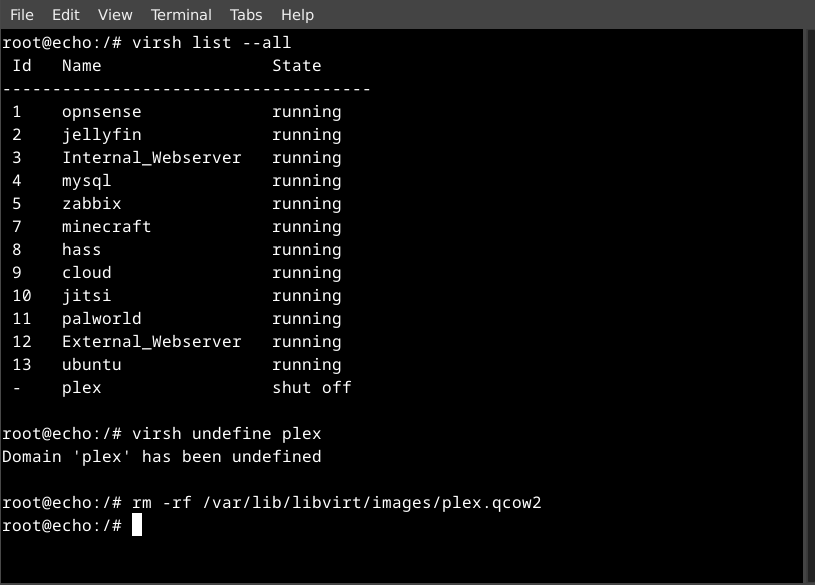
after almost 15yrs my plex server is no more. jellyfin behind nginx with authentik is running very nicely.
A place to share alternatives to popular online services that can be self-hosted without giving up privacy or locking you into a service you don't control.
Rules:
Be civil.
No spam.
Posts are to be related to self-hosting.
Don't duplicate the full text of your blog or readme if you're providing a link.
Submission headline should match the article title.
No trolling.
Promotion posts require active participation, with an account that is at least 30 days old. F/LOSS without a paywall has exceptions, with requirements. See the rules link for details. Tags [CBH] or [AIP] are required, see the links in Rule 8 for details.
AI-related discussions and AI-involved promotional posts have additional requirements for tagging, as noted in Rule 7 and the AI & Promotional Post Expanded Rules post, and find example disclosures here.
Resources:
Any issues on the community? Report it using the report flag.
Questions? DM the mods!
after almost 15yrs my plex server is no more. jellyfin behind nginx with authentik is running very nicely.
How did you set up Jellyfin with Authentik? Are you using SSO or is it only through LDAP?
i ended up doing both. ldap for the apps. oidc for web based users and the apps that support the quick connect feature. the local user account system works fine too, and ldap would be enough. i just wanted an excuse to play round with sso systems, and it was fun figuring out how to connect all my servers.
authenik has a good docs site for both it's docker container and connecting it to jellyfin. Authelia looked interesting too.
I have been running in parallel both jelly and plex and jelly is good.
Anyone have experience hosting a server for non-technical parents? Plex is just so plug and play and they have clients for even the shittiest old smart TVs.
Anything that has a remote interface is garbage. It's all cursor mouse based except on a few devices.
It's not as good as Plex by a long shot. If you have Plex pass no brainer. If not, I'd personally just buy the pass. On Xbox it was just unusable.
What is authentik and could I use it on podman with compose?
The best and most versatile system is having domains and a reverse proxy that has internal and external domains. Ie jelly.example.com and Vaultwarden.internal.example.com
Then you add authentik which does SSO for many app like nextcloud, immich, linkwarden etc. For apps that don't integrate, you can still use his with reverse proxy authentication (sonarr).
Naturally this is more complex to setup but nothing beats the versatility.
I can choose extra protection for things like vaultwarden (need to connect via wiregaurd). Make things external for other users to access easily (immich, jellyfin, etc). Everything is based on users that are made in authenticatik and they all have the same password with single sign on.
You would approach this is pieces. get the domain and reverse proxy working first. Then authentik. this is only realistic with docker compose.
authentik is an identity server. theres a couple free ones available, this one just worked for me. it provides oauth and ldap fallback for the jellyfin server. along with login for most of the other servers i host like nextcloud/calibre-web/lychee etc. it has a nice easy log in process along with a 'homepage' kinda thing for everything my users can access with their account. makes it easier to support the non technical friends and family.
Its a pre-authentication gateway and SSO provider for OAuth/SAML. So if you dont trust a random docker container to be secure it requires you to authenticate and then it automatically passes a token to the app for SSO if it supports OAuth/SAML.
Foss superiority gang