What’s your go too (secure) method for casting over the internet with a Jellyfin server.
I’m wondering what to use and I’m pretty beginner at this

A place to share alternatives to popular online services that can be self-hosted without giving up privacy or locking you into a service you don't control.
Rules:
Be civil.
No spam.
Posts are to be related to self-hosting.
Don't duplicate the full text of your blog or readme if you're providing a link.
Submission headline should match the article title.
No trolling.
Promotion posts require active participation, with an account that is at least 30 days old. F/LOSS without a paywall has exceptions, with requirements. See the rules link for details. Tags [CBH] or [AIP] are required, see the links in Rule 8 for details.
AI-related discussions and AI-involved promotional posts have additional requirements for tagging, as noted in Rule 7 and the AI & Promotional Post Expanded Rules post, and find example disclosures here.
Resources:
Any issues on the community? Report it using the report flag.
Questions? DM the mods!
What’s your go too (secure) method for casting over the internet with a Jellyfin server.
I’m wondering what to use and I’m pretty beginner at this
We have it open to the public, behind a load balancer URL filtering incomming connection, https proxied through cloudflare with a country filter in place

I use a wire guard tunnel into my Fritz box and from there I just log in because I'm in my local network.
Over the top for security would be to setup a personal VPN and only watch it over the VPN. If you are enabling other users and you don't want them on your network; using a proxy like nginx is the way.
Being new to this I would look into how to set these things up in docker using docker-compose.
Tailscale, with nginx for https.
Very easy, very simple, just works, and i can share my jellyfin server with my friends
I'm just using caddy and a cheap $2 a year .top domain with a $4 a month VPS. Works for my users, I only have 3 users on my server.
I just install tailscale at family houses. The limit is 100 machines.
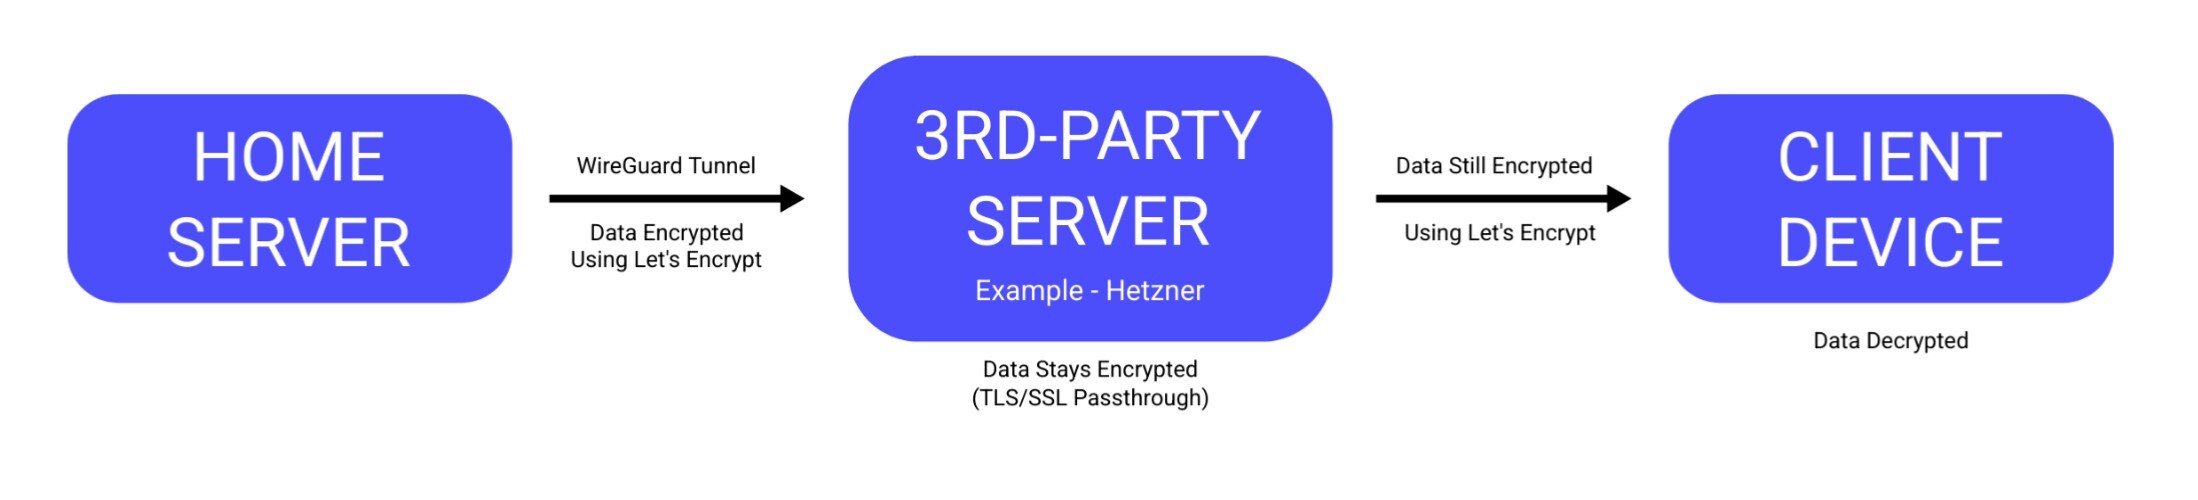
Cheap VPS with Pangolin for Wireguard and reverse proving through the tunnel.
I use a cloudflare tunnel, ISP won't give me a static IP and I wanna keep my firewall locked down tight.
Tailscale - funnel
Just that
Cloudflare. No public exposure to the internet.
Are we not worried about their terms of service? I've been using pangolin
I run multiple enterprise companies through it who are transferring significantly more sensitive data than me. I'm not as strict as some people here, so no, I don't really care. I think it's the best service, especially for free, so until things change, that's what I'm using.
“Technically” my jellyfin is exposed to the internet however, I have Fail2Ban setup blocking every public IP and only whitelisting IP’s that I’ve verified.
I use GeoBlock for the services I want exposed to the internet however, I should also setup Authelia or something along those lines for further verification.
Reverse proxy is Traefik.
Full guide to setting up Jellyfin with Reverse Proxy using Caddy and DuckDNS
I followed this video and modified some things like ports
Personally I use twingate, free for 5 users and relatively straightforward to set up.
I have had Jellyfin directly open to the Internet with a reverse proxy for years. No problems.
I just use tailscale. I am thinking about external share options but for me and my closests just plain simple tailscale
For now just Tailscale but I'm working on setting up a reverse proxy and SSO through Authentik
An $11/yr domain pointed at my IP. Port 443 is open to nginx, which proxies to the desired service depending on subdomain. (and explicitly drops any connection that uses my raw ip or an unrecognized name to connect, without responding at all)
ACME.sh automatically refreshes my free ssl certificate every ~2months via DNS-01 verification and letsencrypt.
And finally, I've got a dynamic IP, so DDClient keeps my domain pointed at the correct IP when/if it changes.
There's also pihole on the local network, replacing the WAN IP from external DNS, with the servers local IP, for LAN devices to use. But that's very much optional, especially if your router performs NAT Hairpinning.
This setup covers all ~24 of the services/web applications I host, though most other services have some additional configuration to make them only accessible from LAN/VPN despite using the same ports and nginx service. I can go into that if there's interest.
Only Emby/Jellyfin, Ombi, and Filebrowser are made accessible from WAN; so I can easily share those with friends/family without having to guide them through/restrict them to a vpn connection.
Wireguard VPN to my fritzbox lets me access my jellyfin.
I don't use jellyfin but my general approach is either:
There are obviously ways to do this all on your own but... if you are asking this question you probably want to use one of those to roll it. Because you can leave yourself ridiculously vulnerable if you do it yourself.
for me i just needed a basic system so my family could share so I have it on my pc, then I registered a subdomain and pointed it to my existing ec2 server with apache using a proxy which points to my local ip and port then I opened the jellyfin port on my router
and I have certbot for my domain on ec2 :)
Jellyfin through a traefik proxy, with a WAF as middleware and brute force login protected by fail2ban