The layout I'm designing around is inline: ISP router, then a small dual-ethernet box doing firewall and DNS filtering, then your LAN. For a start, I'd put OPNsense on a cheap dual-NIC mini PC. You get network-wide blocking through a plugin and a VPN to reach your NAS, and VLANs can wait until you need them. I'm biased, since I'm building a box with that exact layout. What I can't settle: for someone starting out, is an all-in-one box less scary, or does it hide the stuff you'd want to learn?
this post was submitted on 15 Oct 2026
88 points (97.8% liked)
Selfhosted
63050 readers
900 users here now
A place to share alternatives to popular online services that can be self-hosted without giving up privacy or locking you into a service you don't control.
Rules:
-
Be civil.
-
No spam.
-
Posts are to be related to self-hosting.
-
Don't duplicate the full text of your blog or readme if you're providing a link.
-
Submission headline should match the article title.
-
No trolling.
-
Promotion posts require active participation, with an account that is at least 30 days old. F/LOSS without a paywall has exceptions, with requirements. See the rules link for details. Tags [CBH] or [AIP] are required, see the links in Rule 8 for details.
-
AI-related discussions and AI-involved promotional posts have additional requirements for tagging, as noted in Rule 7 and the AI & Promotional Post Expanded Rules post, and find example disclosures here.
Resources:
- selfh.st Newsletter and index of selfhosted software and apps
- awesome-selfhosted software
- awesome-sysadmin resources
- Self-Hosted Podcast from Jupiter Broadcasting
Any issues on the community? Report it using the report flag.
Questions? DM the mods!
founded 3 years ago
MODERATORS
Opnsense on whatever. Plus pihole for DNS/adblock.
I put Opnsense on an Intel Pentium G3220 and it's been rock solid for gigabit.
I bought a firewall appliance based on an Intel CPU, with 4x 2.5gbps Ethernet ports, 8gb ram. Installed opnSense on it and been super happy even since!
A bit pricey the hardware, but it's been totally rock solid for almost two years now.
I have configured unbound with ad blocking on opnSense, and it has every single option I would ever want on it. Amazing stuff.
load more comments
(3 replies)
Not sure how "DIY" you want to go. I've been liking OPNSense though. Running it on an air cooled Protectli box.
Handles a symmetric 2Gbps connection just fine.
load more comments
(5 replies)
A used Lenovo ThinkCentre Tiny M720q mini PC, with the PCIe riser and an Intel chipset (Huawei) dual-10 Gbit NIC, running a pretty basic install of OpenWrt. Has no issue with 10 Gbit throughput, maxes out at about maybe 12 Gbit if you do a full duplex test, which I think may be a limitation of the limited PCIe lanes in the riser.
I got 10 Gbit internet at home, looked at the prices of 10 Gbit routers and noted right out! Built this for maybe $100 in stuff off of auctions.
OpenWRT all the way.
Skynet firewall
PiHole
Stable IP addresses and a private interface for family phones/laptops/pcs
Guest network for nasty Roku TV/peleton
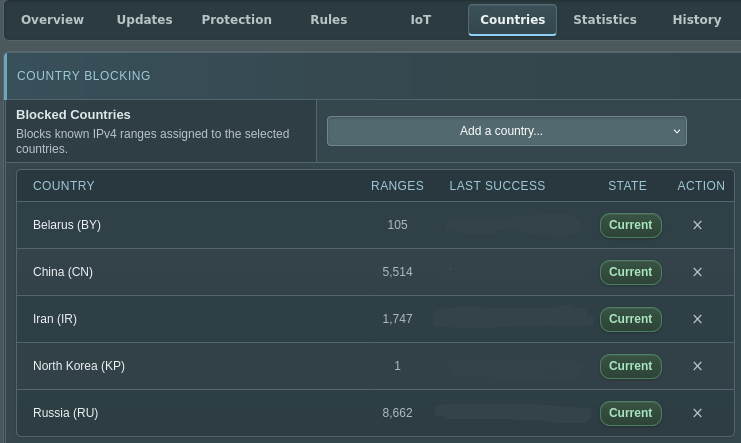
EDIT: my favorite thing about Skynet is the new-ish ability to filter by country
load more comments
(8 replies)
A fanless thin client with Opnsense and a four-port Intel NIC.
This is the way!
Currently running OPNsense on a small Dual-Nic Shuttle PC with an Pentium G4560 and 4 gigs of ram and it's been handling everything I throw at it perfectly fine. Ive got 16 Interfaces, around 10 Wireguard Peers and a SIT tunnel to HE and Im still getting Line Speeds through the firewall.
I’ve never gotten DIY routers including opnsense to give gigabit line speeds once VLANs are enabled.
I usually just use proper network devices. OpenWRT will generally run on anything with Mediatec or Qualcomm based assuming it has support
load more comments
(1 replies)
a minipc with 2 nics running proxmox with opnsense as a vm and one of the nics passed through. that way I can use it for more stuff.
When I retire my desktop PC, the old parts become my router. If you have two network ports, it can do it.
To warrant the power bill, it's also a NAS, NVR, mail server, print server and web server.
All my Wifi APs are various home routers flashed with OpenWRT.
Running an email server sounds super super difficult
I’ve been running mine for over 20 years. It’s certainly got more difficult, especially to be able to reliably communicate with Gmail-hosted servers and outlook.com addresses, but SPF, DMARC, and DKIM are all pretty straightforward to set up. Tightening the encryption/hash algorithms you accept and “anonymizing” your server greetings takes some finesse as well, but I definitely prefer it this way.
I avoid the entire webmail and spam filtering aspects, smtp(s) and imap(s) only.
Not difficult with amazing software like mailcow
load more comments
(1 replies)
I run some china box with 5 integrated 2.5GBe NICs, 48GB RAM and 2x 500GB SSD/NVMe. CPU is Celeron(R) 6305 @ 1.80GHz, two cores or HT, who knows....
On this I run Proxmox. I didn't like Proxmox integrated firewall, so I rolled my own.
all containers unprivileged
one container is the firewall. it has all up+down stream NICs mapped via bridges, cable internet, backup 5g internet on dedicated ports. one port to the switch with a few VLANs, and one bridge that is local to the Proxmox for the local VLANs.
Every service I operate sits in its own network/segment, usually with a /30 netmask. VMs/containers have a eth0 device in this and the firewall defined as default gw. On the firewall the VLAN interfaces are named as the container/service. So the interfaces are not eth0 but wan, wan5g, frigate etc. Great for readability.
Some networks like "family" or "guest" or the one with the APs/WLAN-controller are /24. Bit big, but what ever.
I have a structured netfilter firewall script, fw.sh calling it's parts under fw.d/*fw. Each service is managed individually, sometimes widely open (iptables -A FORWARD -i frigate -o wan* -j ACCEPT) but usually down to the required ports. Database, reverse proxy etc all on separate containers.
There is also like 30 VPN configs from 2 VPN providers. I have a home assistant dashboard where I can direct specific devices to use specifig VPNs. My webradio is routed via UK so I can enjoy BBC2.
root@mercury:~# ip rule show
0:      from all lookup local
20:     from all lookup main suppress_prefixlength 1
300:    from XXX lookup wan_table
310:    from XXX lookup wan5g_table
1000:   from all fwmark 0x1 lookup bbc-ss-lon
1001:   from all fwmark 0x1 lookup bbc-ss-man
3000:   from XXX lookup pm-gb
4000:   from all lookup wan_table
5000:   from all lookup wan_table
5100:   from all lookup wan5g_table
32766:  from all lookup main
32767:  from all lookup default
ip rule also does the fail over to wan5g if required. There are some rules where I tried to auto-filter BBC traffic with marked connections via dnsmasq, but BBC knows all my VPNs (not BBC radio it seems).
IPSec VPNs and other OpenVPNs (dialup, site2site) are handled via a dedicated LXC. There is a tor entry node container, for a few services and one of the public WLANs. Firewall makes sure certain traffic can only exit via certain upstream interfaces, vpn*, wan, wan*... very helpful
I didn't like opensense... don't know why. Work a lot with firewalls in my job (mainly check point, fortigate) so have some professional background.
Also: client isolated WiFi for all iot shit. No internet for TV (jellyfin), PV controllers and most others.
I was using an N100 based mini PC and it did fine at 1gbit. But now that I have 3, and it’s realistically closer to 4 or 5 it doesn’t cut the mustard.
Proper hardware based routers are also just so much more efficient. That N100 machine was constantly hot to the touch. My new UniFi router uses less power and does 10 gig easily.
load more comments
(4 replies)
I had a virtualized PFsense box for a while doing my inherent. Was actually pretty solid even when having to wrangle the quirks having a virtualized firewall/router caused.
load more comments
(2 replies)
OpenWrt on Raspberry Pi 4 with UE300 dongle for the WAN side. 7 years of trouble-free operation so far.
What's the throughput on that bad boi?
I've only tested up to 1Gb. It does 1Gb no probs, with SQM (QoS) which burns a lot of CPU.
Okay cool, thank you
HP Prodesk with some i5 8th gen running proxmox and with a 4x 1gb pcie nic on which a opnsense vm runs.
My DNS was done through pihole. Transitioned now to technitium-dns.
My personal blocklist(s):
https://github.com/Appoxo/Ad-Spam-Blocklist
Contains a list for opnsense (IPs) and technitium-dns (but pihole should be compatible).
Anything else should be mentioned in the readme.
In case of questions, feel free to ask.
It’s currently a N100 mini-pc running Debian, but in the past it’s been all kinds of random hardware including a busted old laptop with an expresscard-PCIe riser for the second NIC. Anything can be a router if you know what you’re doing!
load more comments
(2 replies)
I build a Linux system with multiple NICs. It's heavyweight for a router, and probably not very efficient, but it does the job very well and I love it. I'm using foomuuri to manage the NFTables and NAT and it was very easy (although it's a very obscure piece of software and the documentation and community isn't excessively comprehensive, you might have better luck with something more common but it works nicely for me). It can pull in all the adblocking lists and all that fun stuff. I find it pretty intuitive to configure, at least compared to the horrors of most networking/routing configuration nonsense.
For DHCP I tried using the ISC's new "kea" in the hopes it would be modern and clean alternative to the venerable old isc-dhcp-server but it turned out to be a horrible mistake. They made some awful, insane, unjustifiable design decisions in that software. It gets confused about IP addresses already being claimed (by the exact same host/MAC) address because some arbitrary value changed in how it identifies itself, and then does absurd things with static leases, it just randomly decides to give it a dynamic lease instead, and then will fixate on that dynamic lease and never let it have the static lease back, I fought with it for months, it kept breaking my network for absolutely no reason and it was a nightmare.
Back to trusty old isc-dhcp-server for me. And of course bind for DNS, I'm a bit old-school but it's very comfortable.
dnsmasq might be a lighter-weight and easier alternative you could consider, I think it does DHCP as well, convenient.
And of course, being a full Linux server means you can put all kinds of other stuff on it too. Stuff that needs to be both publicly visible and privately visible on the LAN seems like an obvious fit, but in fact it's probably the worst place to put those services, because you run into issues with NAT hairpinning and other nonsense. For services that are strictly intended for the private LAN/VPN, or services that are strictly public facing, it can handle those just fine by restricting them to a specific interface. But you should avoid stuff that needs to listen on both sides of the connection, it can be done, but it's tricky and annoying and not ideal.
If you need both internal and external access, port-forwarding from the outside through the NAT to another dedicated internal host is a much better solution if possible, it's still a bit tricky (you may have to override the DNS for that domain internally to use the private IP instead of the public one) but it's quite reliable and functional once you have it set up.
None of this is really for the faint of heart, it'll likely require a fair bit of trial and error and physical access to the machine to resolve issues. But it's a fun project and I think the end result is worth it.
load more comments
(1 replies)
i had a cheap made in china consumer router with mt7621 on it, porting openwrt was surprisingly easy and its been running well enough for the past 5 years. adguard home runs on it and handles dns adblocking
load more comments
(3 replies)
Got a “Dell Wyze 5070 extended”, the extended is important because it lets it have a half height PCIe card. Put a dual NIC Intel card in it. It came with 8 GB of RAM and a 64 GB SATA M.2 drive, plenty. Price out a power brick if it doesn’t come with one, which is a Dell laptop one; it refuses to turn on with a PCIe card in and if the power brick is less than 130W (DA130PE1-00 is a product # of it)!! Very annoying. Note the Intel atom processor in it lacks AVX2 instructions which makes mongoDB past v4 not work on it, so you can’t run the Unifi controller, which has vexed me. But it’s fine for internet routing! Never tested throughput but others have online.
(Note: I would not do this now!) I put proxmox on it then did opnsense (passing through the PCIe NICs) and Debian. I chose opnsense over openwrt because opnsense had an automatic update functionality, while openwrt required you to manually wipe the OS and reinstall - when they fix nasty upgrade path that I’ll come knockin. (Openwrt is like that because that’s how routers do upgrades)
I would not choose proxmox now because its upgrade path is fraught since the free level is rolling and they’ve had critical breaking update errors in the past. No good for your router setup. I want upgrades on and automatic so I don’t get kiddie script hacked.
I’m prepping to do either opnsense only and not in a VM or Debian with Incus (VM manager like promox, but not its own OS) installed and then opnsense in a VM. I’m leaning opnsense direct to just make sure my router works, but I’ve never had trouble with Debian yet so still pondering.
I run a pihole and wireguard on the current Debian VM, and opnsense can do wireguard so most of the way there. In the future I’ll switch that pihole instance (wherever it is) to adguardhome, the local rewrite rules in pihole don’t support wildcards so it’s annoying af to have to load in every local domain I set up.
This has worked well for years and I’ve never measured power but I presume it is low.
Hope this infodump helps!
load more comments
(2 replies)
I used to run opnsense on a Xeon blade in my old C6100. It worked well enough but was a waste. Now it’s just a stock ER605 without the Omada controller.
I just put OpenWRT on a (at this point quite old) TP-Link non-DIY home router. The only thing wrong with it is that it isn't a rack-mountable rectangle, which offends my perfectionism.
I don't care if TP-Link thinks it's EOL as long as OpenWRT doesn't. You should check the supported devices list for your current hardware.
load more comments
(1 replies)
I'm running pfsense with wireguard site to site connection between 2 locations. Vlan for my mqtt for my meshtastic. I did have an ad blocker on it but I found it wasn't very good. It was blocking too many things.
Switched to Adguard on my Proxmox instead.
I have a Flint 2 with OpenWRT installed, it handles all my home networking. I have a handful of vLANs and I think the count is still 5 APs. I am currently considering adding a 6th for HA to TV vLAN, one that cannot access the WAN just HA. People have disagreements over OpenWRT and pfsense, or opensense not sure which is the “FOSS” version, but OpenWRT is not going to try and upsell you.
I am sure OpenWRT offers some ad blocking but I already had two finally tuned piholes. There are arguments between pihole and adguard home. I started with pihole I have tried adguard but went back to pihole.
load more comments
(3 replies)
Router is a bunch of old PCs I frankensteined and put opnsense on.
Ended up i5-7500, 8gb mem, 500gb SSD.
Put in a dual-port SFP+ NIC and a dual port 2.5GbaseT nic.
One of the 2.5gb ports goes to my cable modem.
One of the 10gb ports takes Twinax to my dumb LAN switch, the other to my dumb server switch, which right now is really just my storage network...the link to the firewall isn't doing anyt~~u~~hing.
The dumb switches I have here, though, they've got some sort of weird MAC learning disability. It cannot handle macflaps, which I found out about because I had a hard time roaming between APs.
So I got a Netgear GS108T and put OpenWRT on it, and that switches between my APs.
My APs are Linksys MX4200v1's. Also openwrt. Got four of them...one upstairs, two in the ground floor, one in the basement. Can get very close to 1Gbps anywhere in the house on wifi. Not the best platform for openwrt (ipq807x), as I've found out...but it was a hella cheap deal for tri-band AX APs.
load more comments
(1 replies)
OPNsense on used dell optiplex. Very easy but it can do whatever you want to grow into as you learn more.
load more comments
(6 replies)
I got a spiffy little fanless micro PC with five Ethernet ports, installed Ubuntu, and wrote my own iptables rules and installed pihole.
I'm running pfSense on an old Intel Atom fanless mini PC with 6 ethernet ports. I use pfBlocker for ad blocking. I also installed a GPS module in it. That's the clock source for the NTP server. I was planning on replacing it with something newer, but that's not happening until memory prices come down.
I would not recommend using pfSense anymore. My next router will be running OPNsense. I will probably install Adguard Home on that for ad blocking.
load more comments
(3 replies)
view more: next ›