litchralee

joined 3 years ago
[–] litchralee@sh.itjust.works 7 points 1 day ago* (last edited 1 day ago)

In a nutshell, there will not exist any premade, out-of-the-box collaboration platform that works precisely for your use-case. And indeed, for anyone's use-case, because there are so many variables at play. Do you have:

  • to deal with scale of 10-100 people or 100k to 10M?
  • trolls and malicious actors that want to derail your project by bikeshedding?
  • a user base that might not already be skilled at recognizing toxic team members?
  • a legal entity for this project which is required to keep minutes or any other reporting requirements?
  • paid developers around the world, which only use this platform to talk to you, thus it must be secure to store PII?
  • and so on

The reason people think it's easy to choose a collaboration tool is because they see Teams and Slack and think that they can just buy a product (or a FOSS equivalent) and they can hit the ground running. But anyone who has set up a Slack community knows that there are a lot of rules and conventions that have to be established. For example, FTX (the failed cryptocurrency exchange) was using Slack emojis to approve business expenses. Setting aside that example of colossally bad financial controls, every org of any size must establish what their baseline processes are, and that extends to the collaboration platform.

but I don't want to worry about all the moderator tools and restrictions and BS either.

Moderation is not optional. Every non-trivially sized collection of people will end up with disagreements that distract from their joint reason for being there. To not moderate is a choice, as demonstrated most succinctly by this post: https://www.techdirt.com/2022/11/02/hey-elon-let-me-help-you-speed-run-the-content-moderation-learning-curve/

At the very least, the collab platform you choose to use should have some tooling for a future moderator to utilize, so that you don't have to switch platforms the moment someone reveals themselves to be a neo-nazi, starts spamming swastikas into the chat, and you're powerless to do anything about it. For small groups, it's less probable but the risk grows over time.

[–] litchralee@sh.itjust.works 5 points 1 day ago* (last edited 1 day ago)

Is the question in relation to immigration requirements, or for job prospects? For the former, any accredited university will likely not have a problem being recognized, not unless it's a for-profit university or has a sizable "controversies" section on Wikipedia. Online degrees from an established public university generally bear the name of the university at-large, so there'd be no noticeable difference when looking at the diploma.

As for the job prospects, that's going to be very market specific. Perhaps the larger question is whether an online degree or not, is there enough demand in your prospective countries for MEs and EEs that employers are willing to go with a new resident from abroad, rather than from one of the established local universities?

[–] litchralee@sh.itjust.works 1 points 1 week ago

I didn't watch the video -- and YT isn't letting me speed-read a transcript? -- but generally speaking, if you have a need for memory that isn't backed by the filesystem, and you're writing in C, just use malloc. It's designed for that purpose, although malloc might very well be calling to mmap to obtain an anonymous mapping under the hood. Even if you're going to hold on to memory for the entire lifetime of a program, still use malloc in C.

If your application does need some filesystem backing, or if you're allocating enough memory that hugepages might be reasonable, then that's when you'd want to use mmap.

[–] litchralee@sh.itjust.works 3 points 1 week ago* (last edited 1 week ago)

Private party sales of cars in the USA use cash, yes. A fairly safe way to do this for a car is to do the sale in the lobby of the seller's bank or credit union. In specific detail, the buyer arrives and inspects the car to their satisfaction, they fill in most of the vehicle title transfer form but withhold the signature, then they go to the teller where the buyer produces the cash, the teller counts the funds and deposits it to the seller's account, and finally the buyer and seller sign the title transfer.

In this way, the buyer's risk is minimized (they're meeting in a quasi public place with cameras, so gunpoint robbery would be unlikely) and the seller's risk is minimized (they don't even have to handle or count the cash, so a bad buyer can't even rob them after the sale).

Not sure if this would be applicable to OP's situation, but it might be adaptable if the seller's bank is nearby and each party makes their own way to the bank to complete the sale, after inspecting the object.

Note: if instead of cash, the buyer pays with an official or cashier's check, then this whole procedure is still valid because the seller doesn't have to deal with the risk of a bad check: their bank has procedures to verify on-the-spot the funds on an official or cashier's check issued by another institution. For a personal check though, such checks have a TOCTTOU problem, so sellers should not accept such checks for the sale.

[–] litchralee@sh.itjust.works 9 points 1 week ago* (last edited 1 week ago) (1 children)

The CA cannot decypt: they don't have the secret key which only the server has. When requesting a new certificate from the CA, the server generated a secret key (aka private key) and then generated a derived public key that goes into a Certificate Signing Request (CSR). The CSR is what the CA receives, not the secret key, and then the CA returns the certificate file to the server, which has been endorsed by the CA and thus trusted by the user base.

Phrased another way, a certificate is the instrument that confirms that a purported public key can in-fact be safely used, and that no MITM attack is happening (assuming you trust the CA that signed the cert). But once you've confirmed the public key, the rest of the cryptography is public key cryptography, meaning the secrecy of the secret key is the whole game.

[–] litchralee@sh.itjust.works 16 points 2 weeks ago* (last edited 2 weeks ago) (1 children)

I'm deeply skeptical. If the whole premise is that natural language (which is how prompts to AI generation are given) is insufficiently precise to constrain output, and that formal specification is precise enough, then why are we bothering to use natural language generation? If this works as stated, then it's a tactic admission that the thing being checked is inherently flawed. Why not just use the formal specification to generate code then?

I suspect that two things are true: natural language is inherently insufficiently precise for nontrivial code generation, and also that formal specification is not broad enough to describe all the code which is being generated today using AI/LLMs.

Reliability of generated output was never an engineered goal for LLMs, and no amount of "reasoning by Lego" can fully compensate for this no matter how complex the mitigations in post. It's the same reason why safety (under any definition) cannot be "bolted on" to an LLM after the fact.

[–] litchralee@sh.itjust.works 0 points 2 weeks ago

For folks that would like the cosmic distance ladder explained in video format, 3blue1brown sat down with Terence Tao: https://www.youtube.com/watch?v=YdOXS_9_P4U

Yes, it's that Terence Tao, the famed mathematician.

[–] litchralee@sh.itjust.works 5 points 2 weeks ago

The 100 users for the Community edition is more of a suggestion and is not a hard cap, according to this answer: https://github.com/element-hq/ess-helm/issues/1027

[–] litchralee@sh.itjust.works 1 points 2 weeks ago (1 children)

I think Signal tries to be E2EE but has other problems, including that MLS (the E2EE mechanism) inherently requires a client app instead of being usable with just a browser.

I'm having trouble imagining what in Signal's implementation of the Double Ratchet, or any part of RFC9420 Message Layer Security, would inherently require a client app. Perhaps you mean that there is no readily available browser-implemented API for carefully managing secrets? Even in that situation, all the libraries needed to implement the RFC can be compiled as WebAssembly or to JavaScript (with the assumption that the browser and OS are outside a malicious actor's capabilities) and ran that way.

To be clear, I'm not suggesting Signal is perfect, and papers about problems found in Signal and other apps are readily found, like this one from last month. But with that said, it does appear that OP's described use-case involving hundreds of users in group chats is very much not what Signal was designed for,.

[–] litchralee@sh.itjust.works 2 points 2 weeks ago

When examining why corporations toe the line for conservative endeavors, it's less useful to examine the financial aspect and more useful to look at the power dynamic. Oligopolies are like dictators, in that they need to occasionally perform a tour de force, as a way to suppress the exercise of soft power. That is to say, scare the opposition to fragment them and to disorganize them, so they don't get any bright ideas. Inspirational Skeletor warns precisely of this: https://mas.to/@skeletor/117191580571928662

What soft power would Visa and MasterCard have been afraid of? For context, in the USA, debit card transactions are capped at a fixed rate per transaction, whereas credit card transactions can have both a per-transaction and a percentage. Accordingly, the card networks would very much like to be processing more credit transactions than debit. But this revenue comes off the backs of consumers, in the form of higher prices because Visa's fee is rolled in, even for people paying with cash. Enough clamoring about cost of living could easily put the card processors front-and-center before a Congressional committee, a spotlight they don't really want.

Such furore would have to be driven from both consumers and businesses complaining about the extortionate practices by the card processors. Which is why the card networks hide in one domain and attack in another: deflect to greedy banks that are charging high interest directly to consumers (thus ignoring the cut that Visa/MasterCard take), and then clamp down on one segment of businesses, as a sign that they can be vicious if any other businesses start blabbing to the feds.

The card networks assume (unfortunately correctly) that small and medium businesses will not band together to overcome these monopolistic moves. And the largest businesses that process the most card transactions (eg Amazon, Walmart) are so entrenched in accepting card payments that they already negotiate deals directly with Visa and MasterCard, so they're not a risk.

In the end, this could be viewed as a conservative cause that happens to overlap with a need for a naked show of force. And in that endeavor, they've succeeded: every platform that takes cards is on heightened alert, and that's a real chilling effect on the marketplace. What Visa and MasterCard can do to one business segment, they can do to any other. But I guess for now, most businesses are just pricing that in as yet another "cost of doing business".

[–] litchralee@sh.itjust.works 42 points 2 weeks ago (8 children)

In a nutshell, an Australian anti-porn group put pressure on the credit card networks Visa and MasterCard, which process the grand majority of card payments worldwide, for both credit and debit cards.

https://www.thepinknews.com/2025/08/04/visa-mastercard-adult-purchases/

What remains unclear to me is why a somewhat obscure lobbying group was able to bring two American multinationals to heel. But in any case, I am of the opinion that this group sits well within the range of right wing reactionary, in spite of dressing itself up in the cloak of feminism. The group's Wikipedia page lists the founder as a conservative and anti-abortion activist.

As usual, Wilhoit's Law is instructive: this despicable group seeks to denigrate sex work, depictions of sex, and the legal market for sex art and anything arbitrarily similar, by denying this group of people from the financial system and from earning an income, and then leave them without any support or even a suggestion as to what these people should do instead. This is the "bind but does not protect" part of Wilhoit's Law. No different than American conservatives and TERFs that try to drive a wedge to isolate trans people, this group targets sex workers and they cannot be allowed to continue unabated.

The legal solutions are as straightforward as they seem: require that interstate financial services can only charge a fee if transactions are routed and processed neutrally. The economic solution would be the expansion of existing national payment clearing networks (ie ACH in the USA) to also process card payments as an alternative to the duopoly.

[–] litchralee@sh.itjust.works 4 points 2 weeks ago* (last edited 2 weeks ago)

IMO, Leetcode and other programming exercises are a simulacrum for assessing aptitude. The exact exercise is not the point -- though many managers might think otherwise -- but rather is the process: can a candidate methodically approach a challenge with sufficient rigor as becoming of an engineer?

I've written before about what I look for when conducting interviews, in the context of embedded software engineers. In that realm, I'm usually probing for prior experience with computer architecture in general, not necessarily in the particular framework that the job will deal in. I want to see transferrable skills, because it's kinda rare to actually find perfect candidates that already meet our final requirements. So instead, I expect candidates to be quick studies, the sort of people that can draw analogies and get an approximate answer. Everything else can reasonably be looked up in man pages and web searches.

But this might just be specific to embedded, where we do actually care about the nitty gritty compiler and assembly details, when there's only 512 KB of RAM. And to be clear, a candidate that knows bit tricks will likely do well, but if that's the only tool in their toolbox and they don't or can't understand why writing maintainable, mostly-portable code is important in a medium sized organization, then that could be a problem. In this realm, programming exercises are still a view into a mindset. Other CS fields may vary.


The convention in the USA for old urban centers and new suburban sprawl is to construct a street or road with a crown that drains rainwater to gutters along both sides of the road, then have storm drains to convey the water from the gutter to some nearby creek or tributary. But why?

Wouldn't it be easier to construct the road in a roughly canal shape, so that rainwater drains towards a single V-shaped gutter at the road's center? This would cut the number of storm drains by roughly half, prevent leaves from falling directly into a drain and clogging it, make it possible to clear a drain by driving a streetsweeper over it, and also prevent a clog from flooding adjacent properties, since the road itself can temporarily impound more water until municipal authorities can clear the blockage (whereas side gutters would invariably flood the sidewalk and carry sharp debris that would damage tires entering a driveway).

Furthermore, a center drain can be built once and then retained as-is each time a suburban arterial needs expanding -- "just one more lane, bro" -- whereas side gutters are regularly demolished and rebuilt to accommodate additional lanes. By routing water away from the edges of the road, sidewalks avoid freeze/thaw cycles, and the road surfacing can be continuous from the curb: no more bike lanes in the gutter. As a convenient benefit, the "drop" off at a curb-cut from a driveway to street level would cease to exist.

And where required to improve water quality due to runoff pollution, a center drain can be excavated and rebuilt as a linear stormwater retention pond, where moderate stormwater can filter into the local soil slowly, with a predefined overflow level that will drain to the existing stormdrain pipes. This is already done for both surface parking lots as well as Interstate highways, so it's not an unproven design.

Narrow alleyways in older cities do use a central drain, so I can't see why the idea stops making sense for larger streets and roads. The only drawbacks I can envision are aesthetic -- a neighbor's excessive lawn irrigation would draw a wet line across half the street -- and that the center channel would also carry leaves and wayward soccer balls into the middle.

But even still, that doesn't seem worse than the status quo: gutters attract all sorts of detritus, but it's usually hidden beneath the wheels of parked cars until something punctures a tire. And at least in water-starved California, irrigation runoff deserves to be noticed and called out so that it gets fixed. There may even be some small road safety benefit from having a V-shape channel in the center, since it would unmistakably divide opposite sides of the street.

For larger arterial roads that have trees in the center, this seems like free irrigation and water pollution control. It even works when the center traffic lanes are converted for running a tram or light rail train.

What am I missing here?


cross-posted from: https://sh.itjust.works/post/61250326

A crafted MeshCore node name could compromise any Home Assistant instance running meshcore-card as soon as someone viewed a dashboard with that card.

The same XSS (cross-site scripting) pattern appears to be present in MeshCore-Home-Assistant-Panel-v2 and its HACS variant

To be abundantly clear, and the post goes into detail why, this is not a bug in MeshCore but rather in how web dashboards are not properly sanitizing untrusted input. In this case, the untrusted input is via a field that any malicious MeshCore node could send.

Well worth a read and a follow on their Mastodon.


A reasonable overview of the MeshCore architecture and tunable parameters.

Probably the only part I don't agree with is the idea that the companion/repeater dichotomy is an inherent part of the MeshCore architecture. I don't believe it is, although it's certainly part of the practical implementation. That is to say, if someone wants to use MeshCore purely as a private point-to-point link, then they can jettison the motions of companions and repeaters entirely. As a person to person mesh network, though, companions and repeaters are essential. The distinction I'm trying to draw is that MeshCore can be a lot more than text messages sent amongst friends.

While reading, the explainer for the three-tier t delay seemed especially analogous to me to how circuit breakers are arranged: a nearby power strip might have a fast-tripping 15 amp thermomagnetic breaker, the upstream main panel might be using a 20 amp curve B (moderate trip rate) thermomagneric breaker, and the utility might be using a magnetic 400 amp breaker. By their nature, thermomagneric breakers will handle localized faults that are 3-5x the rating, while the utility's magnetic breaker will trip precisely at 400.1 amps, to protect line-side equipment. Whereas if the utility breaker tripped first, it would unnecessarily black out a whole neighborhood.

Also observe that MeshCore's "flood-then-direct" behavior is identical to that of Ethernet (ie unknown unicast, then unicast), except that Ethernet frames do not get appended with the network path as they progress, which is akin to the postal service where letters arrive at their destination but with no indication of the routing. Accordingly, the MeshCore sender necessarily reserves space to store the mesh route, choosing a tradeoff between node-count (up to 64) or granularity (up to 3 bytes per repeater). This seems complex, but just like with the tax code, complexity is necessary to handle every reasonable scenario.

I will also reiterate the ongoing bug in MeshCore's encryption, which is the use of AES-ECB in the year 2026. Although it's AES-256, ECB has been a known encryption vulnerability for decades and should not have been used in the MeshCore spec. Meshtastic appears to have avoided this particular foible.

Note: the author's blog mentions in the About page that some AI is used to assist in his writing.


Background: I spent 40 minutes typing up a reply to a different post, but decided that it ran on for too long. I'll include it at the bottom, but I'm curious to know how much cash is still used in this country.

Certainly, a like-for-like Giro (Europe) system doesn't exist in the USA, with ACH, checks, and Zelle almost filling the void -- albeit incompletely -- which I suspect is responsible for the remaining cash utilization. But is that right? Is cash only used for when there isn't another option? Or is it a matter of consumer preference?

I can understand tipping in cash, or paying for a Craigslist purchase in cash. But maybe I'm missing another dimension? Do some folks pay rent in cash? Or taxes? I'm genuinely curious, but please make sure not to dox your finances in the comments.


My original comment

It's annoying when they get suspicious of a 25k USD withdrawal for instance (even if you managed to prove the purpose of such a withdrawal, it remains at the banks discretion whether they'll approve the transaction).

Let's break this down into multiple points:

  1. Suspiciousness of a 25k USD cash withdrawal
  2. Suspiciousness of a $25k USD electronic or check withdrawal
  3. Necessity to "prove the purpose" of any withdrawal
  4. Bank discretion and considerations regarding withdrawals
  5. Necessity of approval by the bank

I don't believe any of these five points are actually issues. As background, cash withdrawals within the USA are still very commonplace, as the country is fairly rather cash-centric when it comes to businesses, due in part to the lack of a system like Giro (Europe) that has both low, fixed transfer costs and can be sent or received by third-parties. The Federal Reserve's ACH system requires established relationships between accounts, whereas Giro does not. Debit card systems aren't a replacement for Giro either. Zelle (USA) is closer, but still isn't quite as full-fledged. Hence, businesses often deal in cash, pay employees in cash, and consumers pay other individuals in cash (eg buying an automobile).

To that end, for point 1, $25k as a cash withdrawal is not a daily occurrence but it does happen. I can't really think of ever paying for a private party used car by check, and such a cash-heavy transaction is often performed at the buyer's bank, so the seller is assured that the cash is good. In this setting, requesting to withdraw $25k cash is ordinary and mundane, if done very rarely. I doubt even prolific car buyers have this problem, but would be open to hearing evidence otherwise.

For point 2, electronic and check withdrawals have even less suspicion than cash, because they always leave traceable evidence. Money laundering concerns are reduced because the entire money trail can be reestablished later, whereas as cash can easily disappear or be "forgotten". To that end, the suspicion isn't about the cash amount but the source and destination. Even a $1 million check is not suspicious, if it's coming from a law firm's client account to a client's personal bank account. That is, again, a thing that happens fairly regularly. More down to earth, people can and do pay housing deposits by check, and property taxes are often drawn electronically. When one or both accounts to a transaction is prominent and established, there is a low probability of money laundering.

Point 3 is often though to be an issue, due to confusion about regulations for bank clerks on when to file a Suspicious Activity Report (SAR). Bank tellers are required to follow Federal Reserve regulations that aim to prevent abuse of the American financial system for money laundering. An SAR must be filled in whenever the teller: a) thinks money may be laundered, or b) the transaction is above the bank's or regulation's fixed amounts. The latter is often pegged at $10k, so this is where people think that it's disallowed to withdraw over $10k. This is not correct.

An SAR is something the teller fills in, and to do that, they might ask the customer some questions about the transaction. For the grand majority of people, the purpose is quite simple: cash purchase of a car, housing down payment, loan for a friend. Would the teller know if the customer is lying? Nope, not at all. But the SAR forms part of a trail of records, so that money laundering investigators can trace funds in the future. But note that the clerk can fill in an SAR for any type of transaction, including checks, and don't strictly need the customer's truthful answers (or any answers) anyway. An obligation to fill in an SAR does not prevent the transaction from going through. It's a speed bump, not a stop sign.

As for the actual stop signs, that's what point 4 covers. A bank obviously cannot allow a withdrawal if it would exceed the customer's balance, or if they don't physically have enough cash, or if the withdrawal is not authorized (ie not named on the account, or PIN not known), full stop. But other situations may arise where the withdrawal must be delayed, either for the bank's own convenience or because the account agreement specifically requires certain holdings times.

I quickly perused a random account agreement for Wells Fargo and the Available of Funds section describes that new accounts (less than 30 days old) will have elongated hold times for withdrawal against newly-deposited funds. This is applied in a first-in-first-out fashion, so only fully-draining the account would incur the longer hold time. In other cases, the bank may take more time but is required to inform you of that, and provide a definite date for when the withdrawal will clear. This verbiage does not distinguish cash vs non-cash, so they're within their rights to delay a check, as long as they obey their own agreement. If this is not tolerable, find a different bank.

Finally, this also gives us some insight into the default behavior for banks subject to Federal Reserve regulations, which is point 5. A bank may not deny a withdrawal of unencumbered, unheld funds (cash or otherwise), except when the bank has actual knowledge that the withdrawal definitely is for laundering. It is, after all, not their money: it belongs to the customer and they are just the regulated custodian of it. A bank can certainly advise a customer not to fall for a pig-butcherint scam, but they cannot block the customer from obtaining their own money back out. They can, as described earlier, apply a temporary, finite-time hold on the funds, but that's it.

To my knowledge, there is no Fed-regulated, FDIC/NCUA bank or credit union that requires pre-authorized approval to access a customer's own funds. I am open to hearing evidence to the contrary, but I don't believe such a thing exists. How would they even stay in business? To be clear from point 4, a bank can certainly ask for a few day's notice to prepare $50k in new $2 bills. But that's easy enough: just call the bank and verbally request the withdrawal, then collect it in-person days later.

Who is disadvantaged by this? Mostly money launderers and con artists trying to abscond with their scam proceeds. But I'd be remiss if I didn't also mention rich people that prefer to suddenly go on vacation and pay for everything in cash. But the system is designed to be no obstruction to those that plan ahead, or are dealing in such small amounts that it's not a big issue. Normal everyday people all share the costs of money laundering, so it's not fair to disadvantage them just so rich people and scammers aren't inconvenienced by their inability to plan ahead. They don't even have to plan ahead: just keep a few racks in the safe.

It is to me, frankly, a non-issue to withdraw money for me or anyone in the working or middle class, because the very issue of being "flagged by US banks" just rarely even a speed bump. And the rich folks have private banks that will gladly give them inordinate amounts of cash to spend.

What exactly is the problem here, specifically?


What can be done

The most glaring problem with MeshCore is that the maintainers do not openly communicate vulnerabilities. Users are left without knowledge of any problems, unable to judge whether to trust MeshCore with their private communication.


Here is the thing about open source, Andy: it isn't yours to fence. You don't get to ride a community's goodwill into a USPTO filing and a paywall. You don't get to turn "we built this together" into "I own this, pay me." That isn't a pivot. That's a rug pull dressed up as a business model.

And here is the thing about the "license check" you shipped: it is a 32-bit djb2 hash of the device's Android ID, XORed with the four ASCII bytes MCPP, hex-encoded. That's it. Thirty-two bits. Less entropy than a decent ZIP password. A first-year CS student could break it. You used Claude to generate the code. We used Claude to read the code. It took 19 minutes. The receipts are one click away.


CLAUDE CODE JUST RICKROLLED ME. I'm working on a project where part of it will involve videos, and in building out the project it created a dummy page, with made up content (relevant to me!) with two video links pretending to be something else and BOTH WERE RICKROLLs.

Note: I'm using a broad definition of "programmer" to include HTML generation, and a broad definition of "humor" that includes Rickrolling. Together, I think this is appropriate for c/programmerhumor. Mods, please remove if not correct.


As background from the Wikipedia page, the Anaheim Transit Network (ATN) was established as a city-sponsored non-profit in 1998 to operate bus lines around the Disneyland resort in California, with private funding from the various hotels in the area to run this public bus system. These hotels are obliged to operate or pay for shuttles to Disneyland as part of their development agreements with the city, presumably to avoid untold amounts of automobile traffic.

As the linked press release says, ATN will shutter its operations on 31 March 2026. The area will still be served by Orange County Transportation Authority (OCTA), the county-wide bus service, but looking at the bus lines near Disneyland, coverage seems non-optimal as a replacement to ATN's service.

Other reporting indicates that the City of Anaheim was unwilling to invest further into ATN (despite earlier indications), nor were the hotel operators.

What I find utterly inexplicable is that these stakeholders -- especially the city -- are not recognizing this fact: data from Q3 2025 shows that ATN fixed-buses moved 96,300 average daily riders. From the same document, the USA's heavy rail systems did not exceed that rate, except in the San Francisco, Washington DC, Atlanta, Chicago, Boston, and NY/NJ areas. Basically, ATN was moving metro rail levels of people on buses.

I shudder to imagine how bad this will be for Anaheim once the closure occurs, where workers, visitors, and all other former riders will need to figure out how to move around Anaheim. Ride share automobiles hardly have enough capacity to absorb even a fraction of the prior riders, let alone more automobiles, even if they all carpooled. And seeing as many visitors to Disneyland use the buses to stay at farther hotels to reduce costs, this is a negative attraction. The difficulty of car-seats on ride share made the buses particularly attractive to transport younger children safely.

Each individual hotel operator made an economic choice to not properly fund ATN, but together they will all lose out. Likewise, I don't see how the City of Anaheim is going to make up the transportation capacity around the Disneyland area. Disneyland itself isn't party to the agreement that funds ATN, but they do contract with ATN to shuttle visitors from a far-flung parking lot. But they too will be impacted if staff and guests can't afford to get to the park.

Everyone is going to be worse off, and no one is stepping up to the plate to keep the buses rolling, when it's clearly the obvious thing to do.


When I moved into my home many years ago, there was this lock-box mounted to the water main on the side of the house. I figured it was one of those used by real-estate agents to store the house key for viewings, but months passed and it still remained there. No one from my buyer's agent's office had a clue what this was, and the seller of the house had already moved out-of-state.

Recently, I had some plumbing work done, and that also included replacing the main water valve for the house, allowing this lock box to come free from the plumbing. Now inspecting it up close, and looking up the model online, I realized that it has an alphabet wheel and uses a three-letter combination.

As it happens, Thanksgiving weekend was upon me, and since I was bored, I figured I'd try all the possible combinations. Just 17,576 possible combinations, how bad could it be?

The most immediate problem was that due to being out in the elements, the dial did not turn easily. It would move, but was rather rough. And since the knob is only ~1 cm diameter, this is an incredibly un-ergonomic endeavor. I had to stop after the first 100 tries, due to the finger exhaustion.

Knowing this would be untenable for the long-run, I decided to build my way out of this problem. Since a combo lock involves making rotations that almost go all the way around, I drew inspiration from rotary telephone dials, where one's finger starts with the intended number and then swivels the dial around.

But whereas a rotary telephone dial only needs 10 positions, I needed to fit 26 positions, one for each letter. I decided on each hole being 17 mm to comfortably fit any of my fingers, but that also dictated the overall diameter of the wheel. But that's good, since a larger diameter wheel means more leverage to overcome the rough lock movement. It also happens to be that this wheel has a diameter of 180 mm, which is just enough to fit in the 200 mm bed of my 3d printer.

Using FreeCAD, I designed this wheel so that it fits around the splines of the lockbox dial, which held remarkably well. I had thought I would need Blu Tack or something to keep it together.

CAD design for lockbox dial wheel

Using this wheel, I'm able to "dial" combinations much quicker using one hand, while holding the lockbox with my other hand to press the lever down to test the combination. This should be good.

(note: some parts of this story were altered to not give away identifying details)

1
submitted 2 years ago* (last edited 2 years ago) by litchralee@sh.itjust.works to c/newpipe@lemmy.ml
 

(fairly recent NewPipe user; ver 0.27.6)

Is there a way to hide particular live streams from showing up on the "What's New" tab? I found the option in Settings->Content->Fetch Channel Tabs which will prevent all live streams from showing in the tab. But I'm looking for an option to selective hide only certain live streams from the tab.

Some of my YouTube channels have 24/7 live streams (eg Arising Empire), which will always show at the top of the page. But I don't want to hide all live streams from all channels, since I do want to see if new live streams appear, usually ones that aren't 24/7.

Ideally, there'd be an option to long-press on a live stream in the tab, one which says "Hide From Feed", which would then prevent that particular stream ID from appearing in the feed for subsequent fetches.

From an implementation perspective, I imagine there would be some UI complexity in how to un-hide a stream, and to list out all hidden streams. If this isn't possible yet, I can try to draft a feature proposal later.


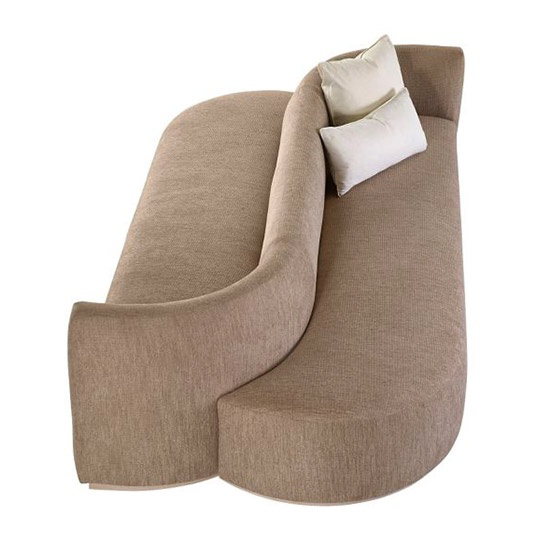
I'm trying to remind myself of a sort-of back-to-back chaise longue or sofa, probably from a scene on American TV or film -- possibly of the mid-century or modern style -- where I think two characters are having an informal business meeting. But the chaise longue itself is a single piece of furniture with two sides, such that each characters can stretch their legs while still being able to face each other for the meeting, with a short wall separating them.

That is to say, they are laying anti-parallel along the chaise longue, if that makes any sense. The picture here is the closest thing I could find on Google Images.

So my questions are: 1) what might this piece of furniture be called? A sofa, chaise longue, settee, something else? And 2) does anyone know of comparable pieces of furniture from TV or film? Additional photos might help me narrow my search, as I'm somewhat interested in trying to buy such a thing. Thanks!

EDIT 1: it looks like "tete a tete chair" is the best keyword so far for this piece of furniture

EDIT 2: the term "conversation chair" also yields a number of results, including a particular Second Empire style known as the "indiscreet", having room for three people!

view more: next ›