I was going to comment a joke saying that it must have been "Iminacult1234" only to find out that it was actually a reference to her cult. She shouldn't be anywhere near power.
this post was submitted on 11 May 2025
281 points (99.0% liked)
politics
31158 readers
18 users here now
Welcome to the discussion of US Politics!
Rules:
- Post only links to articles. Title must fairly describe link contents. If your title differs from the site’s, it should only be to add context or be more descriptive. Do not post entire articles in the body or in the comments.
Links must be to the original source, not an aggregator like Google Amp, MSN, or Yahoo.
Example:
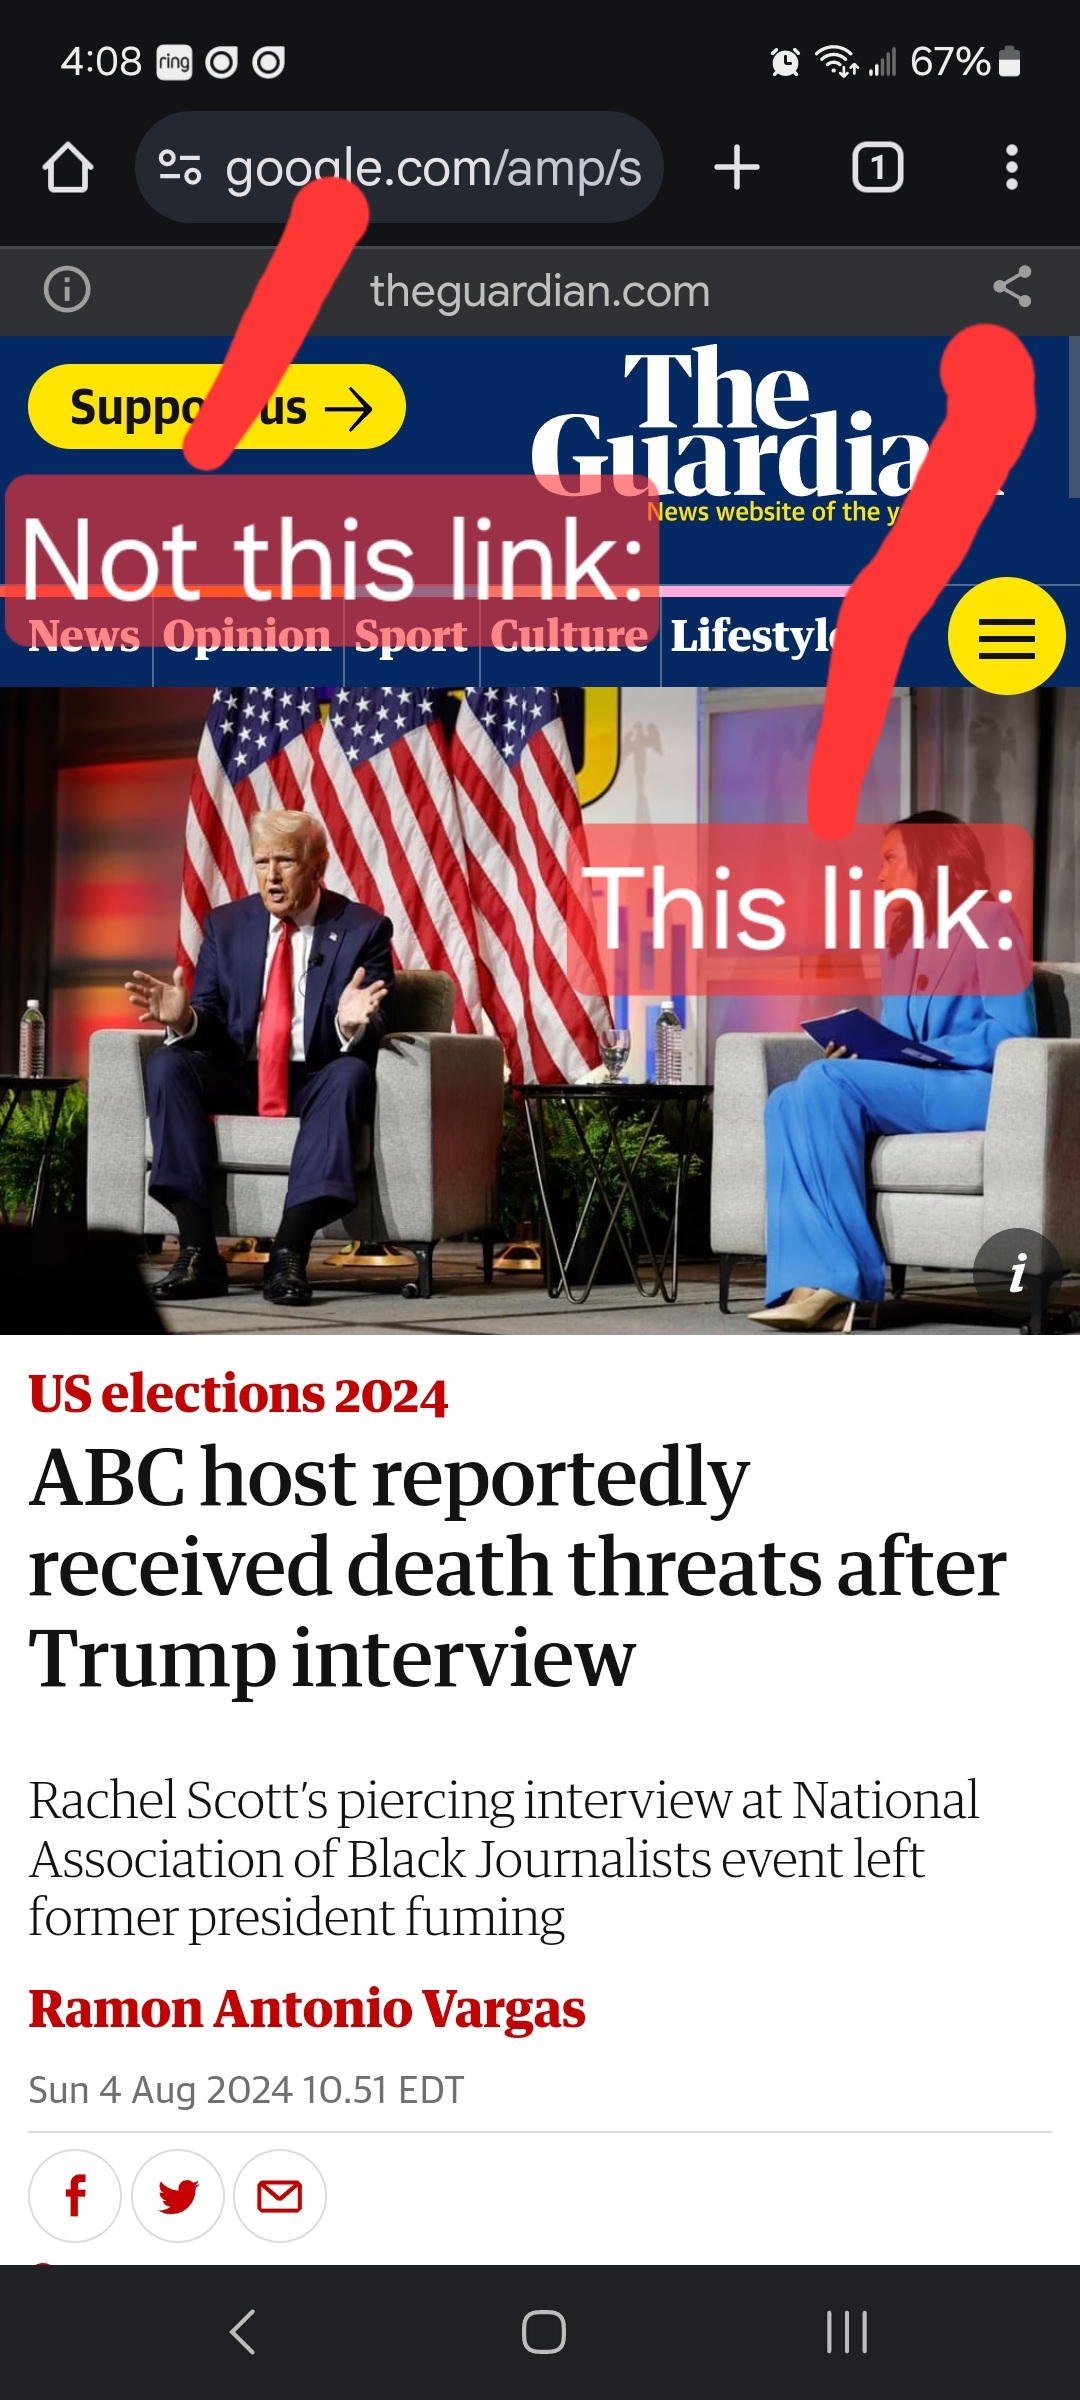
- Articles must be relevant to US politics and contain quality and original content. Social Media adjacent hosts like Substack are allowed, but ONLY if they tie back to a company/subsidiary. No personal or friend group blogs and no self-promotion. Articles should be worth reading. Clickbait, stub articles, and re-hosted or stolen content are not allowed. Check your source for Reliability and Bias here.
- Be civil, No violations of TOS. It’s OK to say the subject of an article is behaving like a (pejorative, pejorative). It’s NOT OK to say another USER is (pejorative). Strong language is fine, just not directed at other members. Engage in good-faith and with respect! This includes accusing other users of being bots or paid actors.
- No memes, trolling, misinformation, or low-effort posts/comments (including reposts). If you see posts like this that anger you, do not engage. Report, block, and live a happier life than they do. Any slap-fight is subject to comment removals. Fights full of rule violations will result in temporary bans to cool off.
- No manipulating votes via bots or alt accounts; this will result in permanent bans. Vote based on comment quality, not agreement. This community aims to foster discussion; please reward people for putting effort into articulating their viewpoint, even if you disagree with it.
- No hate speech, slurs, celebrating death, advocating violence, or abusive language. This will result in an account ban. Usernames containing racist, or inappropriate slurs will be permanently banned.
We ask that the users report any comment or post that violate the rules and use critical thinking when reading, posting, and commenting. Users that repeatedly have comments or posts removed, weaponize reports, or violate the code of conduct, will be banned.
All posts and comments will be reviewed on a case-by-case basis. This means that some content that violates the rules may be allowed, while other content that does not violate the rules may be removed. The moderators retain the right to remove any content and ban users. The reason(s) behind moderator action(s) are publicly available through the Modlog.
That's all the rules!
Civic Links
• Congressional Awards Program
• Library of Congress Legislative Resources
• U.S. House of Representatives
Partnered Communities:
• News
founded 3 years ago
MODERATORS
The password to her luggage is 12345
Shit, I need to change the password on my luggage....
(That joke hasn't aged well, because the TSA has keys to unlock all our luggage now....)
You can just jam a ballpoint pen through most zippers then zip back over it to reclose leaving the lock undisturbed.
Yeah. A zipper on luggage you care about, is pretty stupid.
Those locks were never very secure in the first place.
Only if you use a TSA lock. And those TSA keys started as a collection of keys that were just commonly reused across locks, so people kept them around.
I'm pretty sure the keys got leaked online and you can 3d print copies for yourself
When you have a model number or entire brands or multiple brands that are all keyed alike and sold publicly, it hardly counts as a leak. You could go to Walmart and find them there too. Even before they were called TSA keys.
So the combination is one, two, three, four, five. That's the stupidest combination I've ever heard in my life! That's the kinda thing an idiot would have on his luggage!
Holy shaddrah these people are bad
User: tgabbard
Password: missskunkystripe666
Blyat!
Of course she did. She doesn’t want to make it hard for Putin.
Buttery males!
russiarules12345
Surely they are making a fuss, who would be interested in targeting the head of national security to one of the biggest countries (and most hated by easterners) on Earth?
I knew it. I'm surrounded by assholes!
National what?
Meh, I use the same super-weak password for tons of sites I don’t give a flying fuck about.
I took all the military opsec and infosec courses, because I was in intel, and my partner is currently an IT security professional, but some accounts just don’t warrant giving a damn.
I don’t use it for anything important, I let my password manager handle those, but bullshit “create an account to checkout” stuff that I use another payment system for? Meh.
This doesn’t seem like news, beyond looking for something to report on.
(There is no indication that she used the password on government accounts.)
Why do we care then?
MOST PEOPLE re-use passwords for everything. Most people use the most-used passwords in every data breach as their passwords. Stuff like this shouldn't surprise anyone. Most members of government likely don't even know what 2FA is, and likely use Password123 as their password. They're not known for being tech wiz's.