
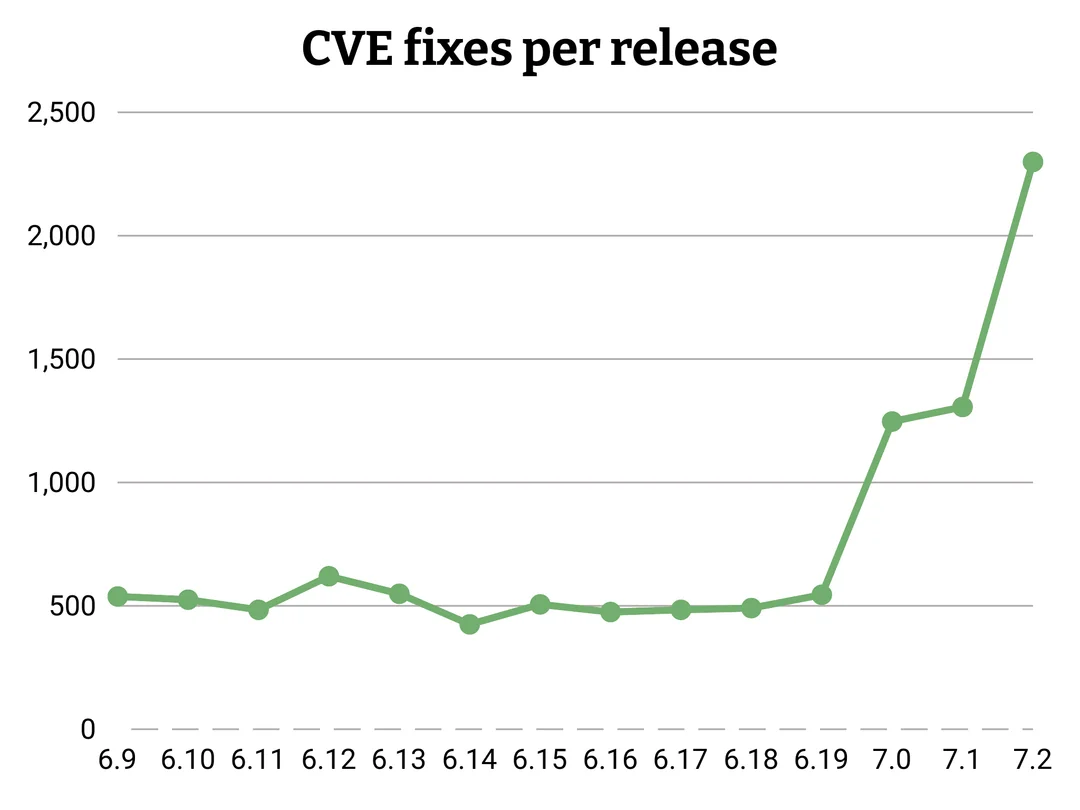
AI coding tools are pretty good at finding bugs and make it easier and faster to fix them.
Importantly, security vulnerabilities in new releases seem to stay roughly the same and the change to which bugs count as CVEs was around version 6.8 already.
A community for everything relating to the GNU/Linux operating system (except the memes!)
Also, check out:
Original icon base courtesy of lewing@isc.tamu.edu and The GIMP
AI coding tools are pretty good at finding bugs and make it easier and faster to fix them.
Importantly, security vulnerabilities in new releases seem to stay roughly the same and the change to which bugs count as CVEs was around version 6.8 already.
ai, protecting people from ai.
yes, you need to find the vulnerabilities before the hackers and it just so happens that LLMs aren't terrible at it.
I think dusk means it would also be difficult for hackers to find these bugs without AI, which probably is true (given how long some of them seem to have existed). Hard to say how it balances out in the end though.