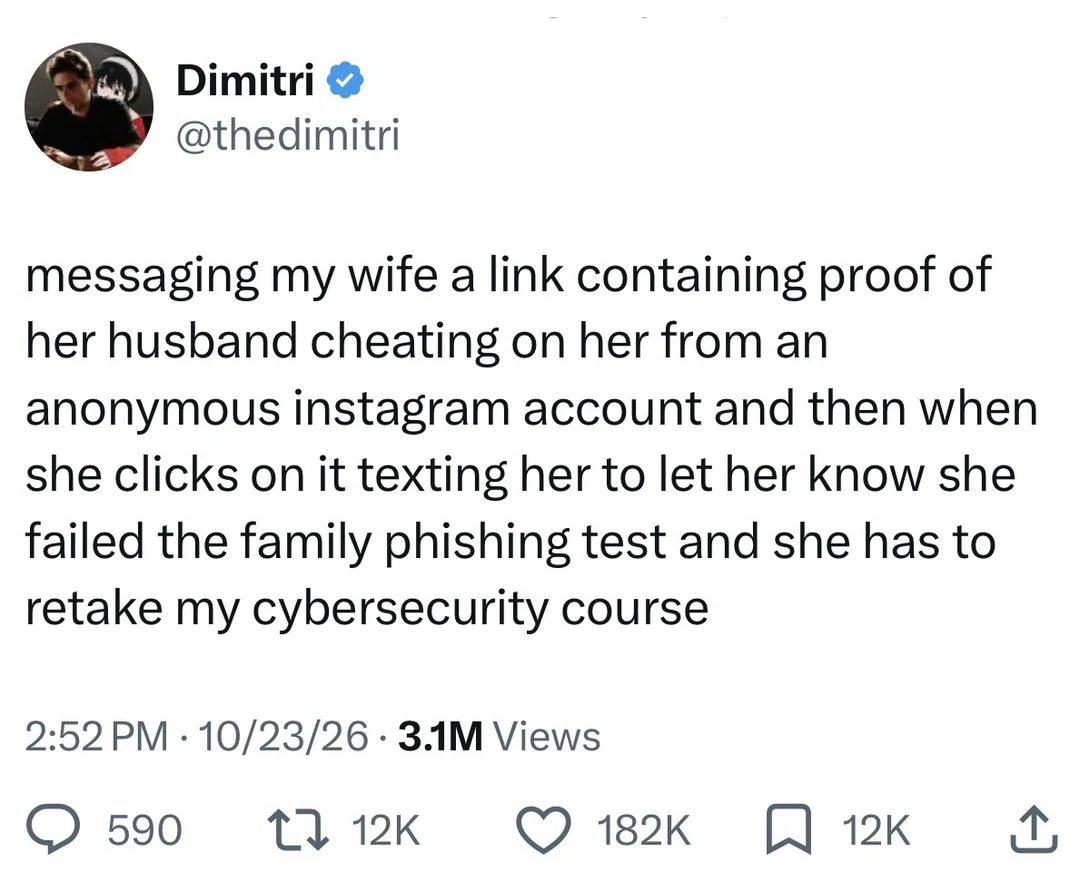
It's a honey pot of a different color! Genius!
Welcome to Programmer Humor!
This is a place where you can post jokes, memes, humor, etc. related to programming!
For sharing awful code theres also Programming Horror.
It's a honey pot of a different color! Genius!
You have chosen Death by chancla
His wife is not Italian. If she was he would not even dare to do anything of the sort.
All these people setting up filters don't understand it is supposed to train you in case a real phishing attempt is made.
Those filters aren't going to stop real ones.
But if you want to blow up the database server you need to work on because you couldn't be bothered to click a button when a phishing test comes around, then you better quit your job in tech.
I swear, developers are some of the biggest security concerns in any company. They complain the moment some access is blocked for good reason. Much bigger concern than old nancy "never-had-a-computer-at-home" clicks-a-lot.
If the fake phishing emails can be caught by my very rudimentary filter they weren't particularly good anyway. Besides, I still have to look at those emails and report them, otherwise my IT still counts it as a strike against me. Win-win. IT continues to keep me on my toes and I don't have to take another 30min training course because I ignored an email for a day or two.
Sounds kinda like the Tale of Foolish Curiosity from Don Quixote. Spoiler: the wife was a good woman and wouldn't have cheated on the guy... until he started being an asshole by subjecting her to endless tests to prove her virtue.
I've been meaning to read Don Quixote and this is the tipping point. I want to make quixotic references.
Just don't read the mails and you won't get fished
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
Oh man y'all remember the actual phishing campaign of messages from customer-service@bankofarnerica. com?
So what do you do when you get an actual phishing mail that doesn't use that TLD?
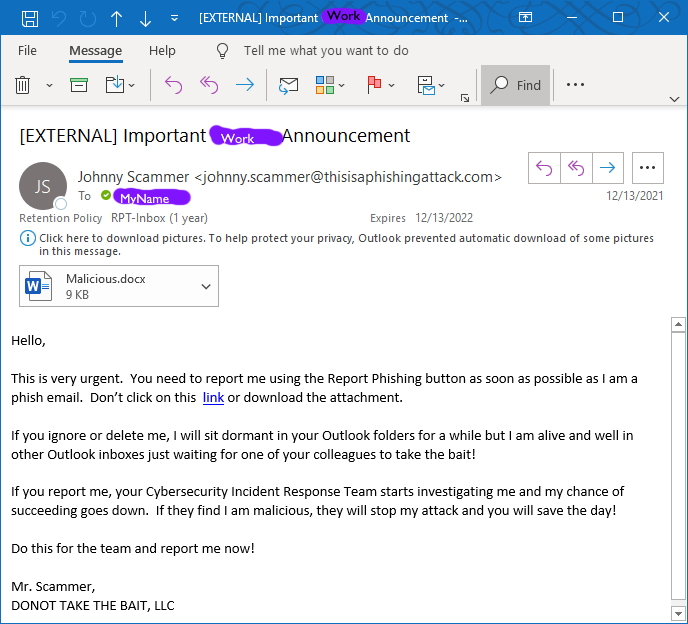
An actual email sent by my company. (not representative of their usual)
I delight in reporting genuine emails from my company that look like sophisticated phishing attempts, bonus points if they send a follow-up assuring us that the previous sketchy email was in fact genuine.
That’s a crack it open with a hex editor, find who sent it, delete then return a note to the sender letting them know you’ve removed the problematic communication, thankyouverymuch.. signed ABiggerCuntThanYou@WhyIsMyCompanyWastingMoneyOnThisShit.org
That's how you get assigned to IT overflow tickets, NGL. 😅
Yeah if anyone falls for this lock them out of their computer immediately.
Clearly he's trying to trick you into pressing the "Report Phishing" button, which must be some sort of a trap. I'd check the attached document for further clues, especially since he's telling me not to. Must be something interesting there
That's pretty cool. Gets the point across - and the reason and results of why it matters to report instead of ignore. Kudos to your team.
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet.
A company I was in a few jobs back had several layers of IT department, there was the local studio department that handled our everyday stuff and a "head office" somewhere far away that set policy and handed out budget and whatnot.
One day "head office" IT decided it was a good idea to send out some fake phishing emails to "test" us. They didn't tell the local IT department about it, I guess they were also being "tested". My manager received one and only recognized it as a phishing attempt after he'd clicked just one too many things for it to feel safe to ignore. So he yanked the power on his computer and contacted the local IT department, as is protocol when something potentially dangerous just happened.
The local network went into lockdown while local IT tried to figure out if something actually dangerous had happened. It cost the studio as a whole several hours of work time, which for a studio our size translated to an obscene dollar cost. Nobody on our side of things did anything wrong, even that one extra "dangerous" click my manager did wasn't something he could be blamed for - head office had crafted the fake phishing attempt well and his reaction to it would have prevented damage had it been real.
Head office never tried a stunt like that again.
Note that at no point does he claim this "proof" is falsified.
Just read this to a beautiful woman I know.
Her response: That's not going to end near as well/funny as you think/hope it will.
Neither is your future if your wife maintains such easily exploited vulnerabilities.
Blink 8 times if you're in danger
Blink 182 times if it's just all the small things
Did they make a song about that?
My knee jerk reaction is to calmly explain why this isn't appropriate in a corporate environment.
I'm so broken.
I saw one with a bunch of maga triggers. The Democrats are doing what!? 😱 they click every time.
I failed one of those because I have script blockers on my browser and I wanted to see what the scam was.